A real-world WordPress security investigation into SEO spam, unauthorized pages, vulnerable components and hosting security risks
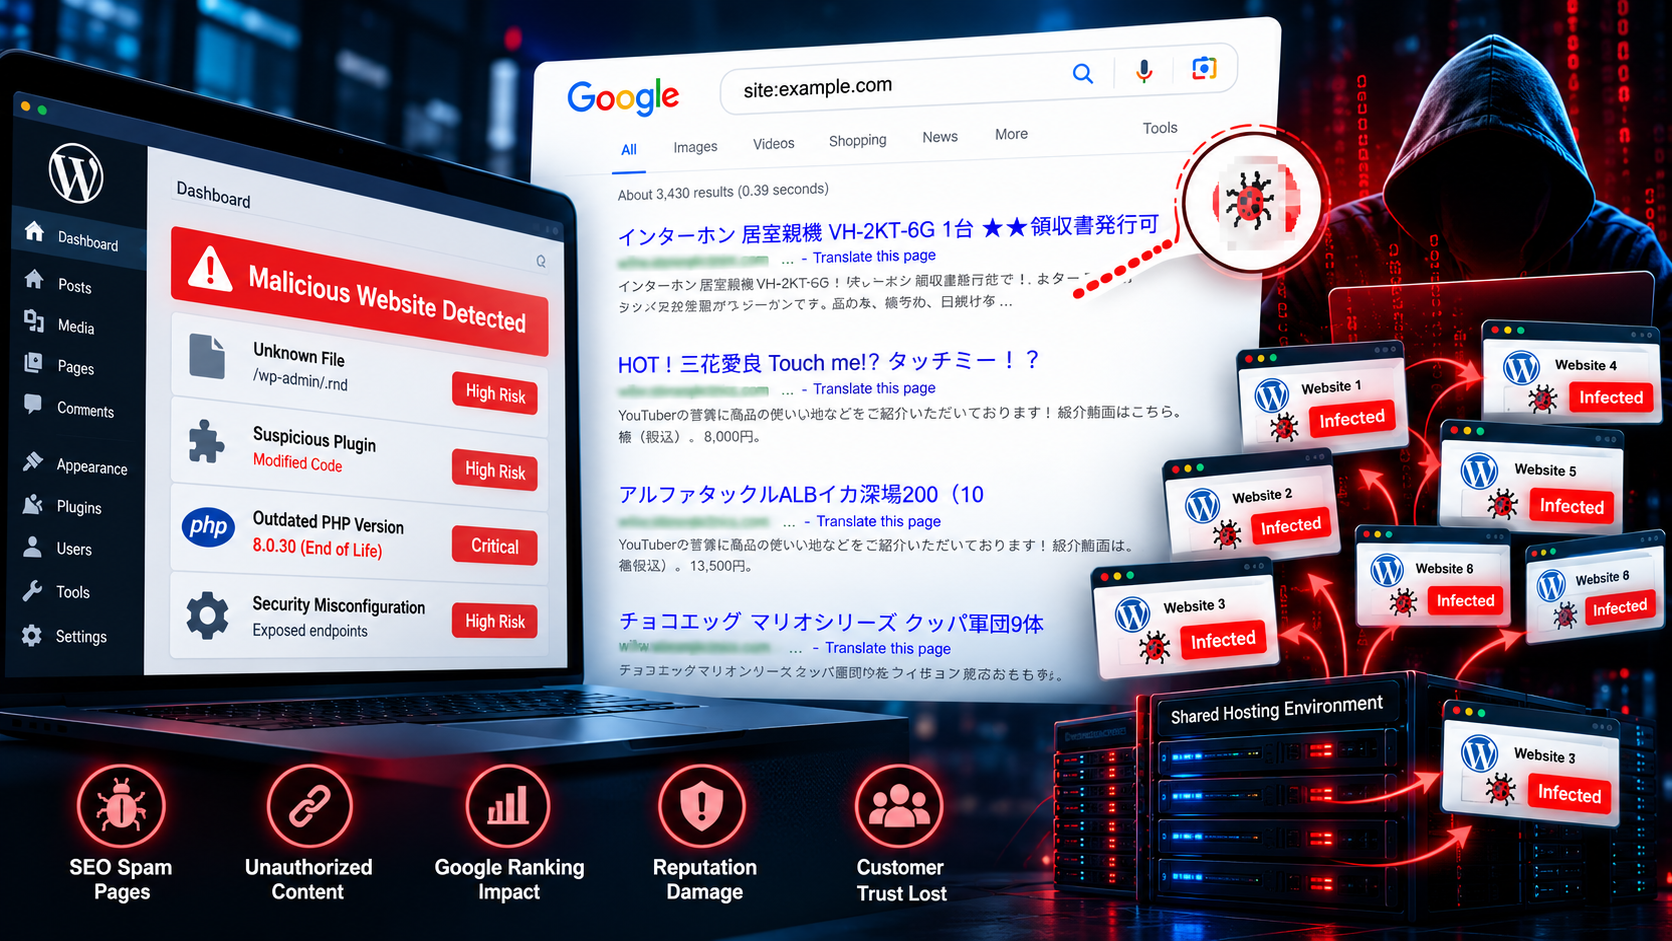
A website can look completely normal to its visitors while being compromised underneath.
In a real-world security investigation conducted by CyberNexora, multiple WordPress websites operating within the same hosting environment were found to have serious security and SEO-related concerns.
The most visible warning was not a broken homepage or a “Hacked” message.
It was something much more subtle:
Unrelated Japanese-language spam pages were appearing in Google Search under a legitimate business domain.
This type of incident is commonly associated with WordPress SEO spam, SEO poisoning and hacked website content.
And it highlights an important reality:
A website does not have to go offline to be compromised.
The Case at a Glance
| Area | Details |
|---|---|
| Technology | WordPress |
| Environment | Shared hosting environment |
| Primary Concern | Unauthorized SEO spam / injected content |
| Observed Content | Japanese-language and unrelated product pages |
| Security Concerns | Vulnerable components, outdated software and configuration weaknesses |
| Assessment Approach | Vulnerability Assessment + Manual Security Investigation |
| Business Risk | SEO visibility, customer trust, brand reputation and security |
What Happened?
The affected websites were legitimate business websites built on WordPress.
During the investigation, suspicious pages unrelated to the original businesses were discovered.
A Google search for an affected domain showed Japanese-language pages and unrelated product content appearing under the legitimate domain.
This is a major warning sign.
The business had invested time and money into:
- Website development
- SEO
- Content
- Google visibility
- Brand reputation
- Customer trust
Yet unauthorized content was being associated with the same domain.
The website could still appear normal when someone directly visited the homepage.
That is what makes this type of compromise dangerous.
How a WordPress Website Can Become an SEO Spam Platform
Attackers do not always need to replace the homepage.
Instead, they may attempt to create or modify hidden parts of a website and use the domain to host unwanted content.
Common examples include:
- Unauthorized spam pages
- Japanese SEO spam
- Fake product pages
- Pharmaceutical spam
- Gambling content
- Fake landing pages
- Malicious redirects
- Hidden links
- Doorway pages
The original website may continue functioning while these unauthorized pages remain active.
In other words:
The website works.
The business operates.
But the attacker is abusing the domain.
Why WordPress Websites Can Be Targeted
WordPress itself is not inherently insecure.
The security of a WordPress website depends on the complete environment surrounding it.
A typical WordPress deployment includes:
WordPress Core → Plugins → Themes → PHP → Database → Hosting → Admin Accounts → Configuration
A weakness in any important component can increase the attack surface.
Common causes can include:
- Outdated WordPress versions
- Vulnerable plugins
- Vulnerable themes
- Nulled or cracked plugins
- Nulled themes
- Weak administrator credentials
- Poor access control
- Unsafe file permissions
- Outdated PHP
- Misconfigured hosting
- Unnecessary exposed services
Cracked & Nulled WordPress Themes and Plugins
One of the biggest risks for WordPress websites is the use of unofficial, cracked or nulled themes and plugins.
A legitimate plugin may provide a useful feature.
A modified version may contain additional code that the website owner never intended to install.
Depending on the compromise, malicious code may introduce:
- Backdoors
- Webshells
- Malicious PHP code
- Unauthorized administrator accounts
- Spam injection
- Redirects
- Unauthorized file creation
The website owner may think:
“I installed a premium plugin for free.”
An attacker may see:
“I found an entry point.”
For a business website, the cost of a legitimate security-tested component can be far lower than the cost of recovering from a compromised website.
The SEO Impact of a Hacked WordPress Website
The biggest damage is not always visible inside WordPress.
It can appear in Google Search.
When unauthorized pages are indexed under a legitimate domain, several business problems can occur.
01 – Brand Reputation
Customers may find strange pages associated with your company domain.
02 – Loss of Customer Trust
A visitor who sees unrelated spam content may immediately question whether the website is trustworthy.
03 – SEO Disruption
Unauthorized pages can create irrelevant indexed content and interfere with the website’s legitimate search presence.
04 – Security Warnings
Depending on the nature of the compromise, search engines or browsers may identify the website as potentially unsafe.
05 – Business Impact
If customers stop trusting the website, the impact can extend beyond SEO into leads, sales and reputation.
The Most Important Warning Sign
One of the strongest indicators observed during the investigation was the appearance of unrelated Japanese-language content under a legitimate business domain.
This is an important lesson for business owners:
If Google is showing content that your company never published, don’t treat it as an SEO problem alone. Investigate the website’s security.
It Was More Than an SEO Problem
The broader security assessment also identified significant technical vulnerabilities on an assessed target.
The vulnerability scan reported:
4 Critical
3 High
4 Medium
1 Low
Total: 12 detected vulnerabilities. alohakidsclinic_va_report-1 (1)
The findings included multiple PHP vulnerabilities, an unsupported PHP version, SSL/TLS weaknesses, FTP cleartext authentication and information disclosure. alohakidsclinic_va_report-1 (1)
The assessment specifically identified PHP 8.0.30 as End-of-Life, with the report listing November 26, 2023 as its EOL date. alohakidsclinic_va_report-1 (1)
Another finding involved unencrypted FTP cleartext login, creating a risk of credentials being exposed during transmission. alohakidsclinic_va_report-1 (1)
This demonstrates an important principle:
An SEO compromise can be the visible symptom of a much larger security problem.
Shared Hosting: Why Isolation Matters
Multiple websites were operating within the same hosting environment.
Shared hosting is not automatically insecure.
However, when several business websites operate within the same environment, proper isolation becomes extremely important.
A business should ask:
“If one website on this hosting environment is compromised, how well are the other websites isolated?”
Poor isolation can potentially increase the risk of lateral impact between websites, depending on the hosting architecture and permissions.
For businesses managing multiple WordPress websites, hosting security should therefore be included in the security assessment.
How CyberNexora Investigated the Incident
CyberNexora did not treat the issue as a simple “remove the spam pages” problem.
The investigation followed a structured security approach.
01. Reconnaissance
Mapping publicly exposed assets and entry points.
02. Technology Identification
Identifying WordPress, themes, plugins, PHP and server-side technologies.
03. Vulnerability Assessment
Identifying known vulnerabilities and security weaknesses.
04. Manual Validation
Where authorized, validating the practical impact of identified weaknesses.
05. File & Content Investigation
Checking for suspicious files, unauthorized content and abnormal website behavior.
06. SEO Investigation
Checking whether unauthorized pages or spam content had entered search-engine indexes.
07. Risk Assessment
Prioritizing findings according to severity and potential business impact.
08. Remediation
Addressing identified security weaknesses and removing unauthorized content where applicable.
09. Re-Test
Testing the environment again after remediation to verify that the identified issues had been addressed.
Why VAPT Matters for WordPress
A common question from business owners is:
“My website is working perfectly. Why should I test it?”
Because:
Working ≠ Secure
A website can:
Load normally → Accept customers → Process inquiries → Rank on Google
and still contain security weaknesses.
A VAPT helps identify vulnerabilities before they are discovered and abused by an unauthorized attacker.
For WordPress, security testing should go beyond simply checking whether the homepage loads.
The assessment can include:
- Authentication
- Authorization
- Admin functionality
- WordPress plugins
- Themes
- File uploads
- APIs
- Database exposure
- Access control
- Server configuration
- Security headers
- Known vulnerabilities
- Information disclosure
- Backup and security controls
The Business Risk Chain
A website compromise can create a chain reaction:
Website Vulnerability
↓
Unauthorized Access
↓
Malicious Content
↓
Google Search Spam
↓
Customer Trust Issues
↓
Brand Reputation Damage
↓
Potential Business Loss
That is why cybersecurity and SEO cannot always be treated as completely separate areas.
Your SEO builds the reputation of your domain.
Your cybersecurity protects the platform behind that reputation.
Key Lessons From This Case
01. A working website is not necessarily a secure website.
02. WordPress plugins and themes are part of your attack surface.
03. Nulled and unofficial components can introduce serious security risks.
04. SEO spam can be a symptom of a deeper website compromise.
05. Shared hosting requires appropriate security isolation.
06. Outdated server software increases security exposure.
07. Regular security testing can help identify weaknesses before attackers do.
Final Takeaway
Businesses can spend months building:
SEO rankings.
Content.
Backlinks.
Brand authority.
Customer trust.
But if the website behind that investment becomes compromised, attackers can abuse the same domain the business worked so hard to build.
Your SEO investment protects your visibility.
Your cybersecurity protects the platform behind it.
A professional website security assessment is therefore not simply about preventing a “hack.”
It is about protecting:
Your Website.
Your Data.
Your Google Visibility.
Your Reputation.
Your Business.
CyberNexora – WordPress Security & VAPT
CyberNexora helps businesses identify and address security weaknesses through:
Web Application VAPT | WordPress Security Testing | API Security Testing | Cyber Security Audit | Network Security Assessment | Cloud Security Assessment
Don’t wait for attackers – test your website before they do.
CyberNexora
Security Testing. Risk Assessment. Better Protection.